
AI
Lens
Gain visibility, govern and secure GenAI usage across your workforce and coding agents.

AI Lens gives you visibility into every AI service in use, lets you govern access by role, and protects prompts and responses in real time for your workforce and your coding agents.
Shine a light on workforce shadow AI
Employees and developers use public AI services, embedded assistants, coding agents, and personal scripts to get work done. Security teams need to know which tools are in use, who is using them, and where sensitive information may be exposed.
Get the visibility you need to close gaps without blocking progress.
Apply role-based policies aligned with risk
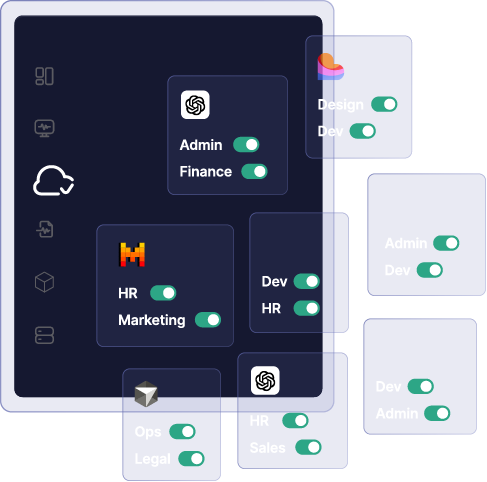
Define who can use specific AI services and coding agents. AI Lens integrates with your Identity Provider (IdP) to apply access policies that reflect each team's needs.
Control which users are allowed to access specific AI services, apply different levels of restriction based on risk, and ensure consistent governance across the organization.
Protect interactions in runtime
Use DeepKeep’s AI Firewall to inspect prompts and responses as they occur. Block unsafe inputs, remove sensitive content, and restrict risky outputs based on your organization’s policies. Controls can be adjusted per user group or tool, giving you the flexibility to support safe adoption while preventing high-risk behaviors.
For coding agents, inspection also covers content accessed through file reads and MCP tools. Detect credentials, tokens, and passwords in the information an agent receives and sends, including content the developer never typed into a prompt.

Stay in control
without slowing down
You don’t need to slow innovation to control risk.
With DeepKeep, you can enable AI across the business while maintaining visibility and control where it matters.
Security stays in control. The business keeps moving.
FAQs
AI Lens helps organizations discover AI usage, enforce access and usage policies, and protect interactions in real time. It covers employee and developer use of AI services, with dedicated controls for coding agents through AI Lens for Developers.
AI services are being adopted rapidly, often without oversight. AI Lens enables continuous discovery of both sanctioned and unsanctioned AI services, helping organizations uncover hidden usage and reduce unmanaged risk.
AI Lens surfaces risks such as sensitive data exposure, use of unapproved AI services, and policy violations, giving security teams a clear understanding of where governance is needed.
It provides discovery across all AI services, including those that are not officially approved, ensuring full visibility into shadow AI usage.
Yes. AI Lens enables organizations to define and apply usage control policies, allowing them to govern which AI services can be accessed, by whom, and under what conditions.
Yes. AI Lens integrates with existing IdP systems, enabling organizations to map AI usage to users and groups, and apply policies based on identity and role.
AI Lens uses existing hooks within supported coding agents to inspect prompts, shell commands, file reads, and MCP tool calls. It applies policy decisions, checks for sensitive data, flags insecure code patterns, and sends destructive commands to the developer for approval.
It provides continuous visibility into AI service usage, helping organizations enforce policies, reduce shadow AI risks, and demonstrate control over how AI is adopted across the business.
Yes. AI Lens operates out-of-band, enabling discovery and policy enforcement without impacting user workflows or introducing latency.
Time to value is measured in minutes. Enterprises can quickly gain visibility into AI service usage and begin applying control policies with minimal effort.